Zero Trust for the critical machines and devices that software cannot secure
Faction Pods, Portals and OutpostsBring everything from PLCs to IP cameras onto your owner-controlled network — reachable by what you need, unreachable from the public Internet. No agents, minimal IT support, no rip-and-replace.
Most OT and IoT devices can't run security agents — they lack the resources for encryption or a programmable interface, or run legacy operating systems that can no longer be patched. Faction protects them anyway: with Pods, Portals and Outposts, or hardware you already own enabled with Canopy.
The hardware already inside your network may be the threat. The FCC has determined that the foreign-made routers common in homes and businesses pose an unacceptable national-security risk, and national cyber leaders have repeatedly warned that state-sponsored actors like Volt Typhoon have pre-positioned widely inside of compromised routers, smart hardware and infrastructure.
Three ways to deploy protection
All deployment options provide the same Faction Network security and owner-controlled cryptographic trust. Hardware provenance and assurance vary by deployment option.
Faction Pods & Portals
Faction purpose built. Faction hardware running Faction firmware: Purpose Built, Assembled in USA, ORION Assured.
See Faction Pods & PortalsFaction Outpost
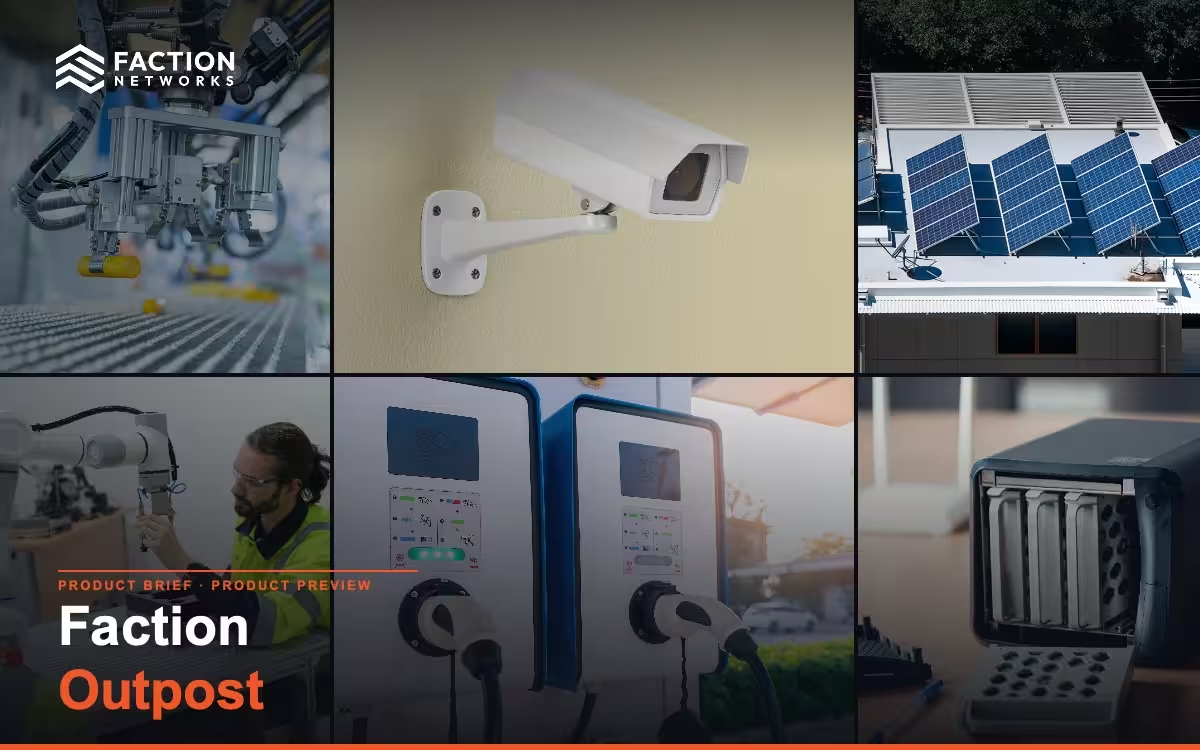
Faction curated. A screened third-party router we prepare, test and ship. Plug it in behind your existing router and adopt it on your local network.
See Faction OutpostFaction Canopy
Customer owned. Keep your hardware. Faction enablement and configuration for compatible hardware you already own.
See Faction Canopy- IP cameras and the video streams they produce
- Industrial controllers, PLCs, and SCADA equipment
- Factory-floor machines — legacy and modern, post-T1 and internet-connected
- Sensors, robots, and automation systems
- Building systems — HVAC, access control, and elevators
- Medical, lab, and diagnostic devices
- Point-of-sale, kiosk, and payment terminals
- Printers, scanners, and network-attached storage
- Smart-office and consumer IoT devices
- Legacy equipment that can no longer be patched
- Any other machine or device that cannot secure itself
Faction protection sits at the local network boundary: on Faction Pods, Portals and Outposts, or on compatible hardware you already own, enabled with Faction Canopy. Protect any connected device — regardless of its age or capability — simply by connecting it behind one, with no software installed on the device itself, and it joins your private, owner-controlled network. That mitigates the threat from compromised routers and smart hardware already sitting inside your network without a rip-and-replace.
Owner-controlled keys
Adoption uses the owner's network key, created and held on the owner's own devices. No one else — including Faction — holds it.
Out-of-band authentication
A direct invitation, authentication, and key-exchange method that isn't exposed to external observation or attack.
Off the public internet
Once adopted, devices behind the Pod are reachable only from inside the network — removing the public-internet attack surface.
No anonymous access
Every device is cryptographically verified before any access — no shared passwords, and no anonymous connections are possible.
Nothing on the device
Protection lives at the local network boundary, so even devices that can’t run software or be patched are covered.
Zero Trust for Hardware
Whichever option you choose, we support only OEMs and models certified by the FCC for sale in the US — none from an entity on the FCC Covered List — and then apply our Zero Trust for Hardware process. How far the hardware assurance goes depends on who built the device.
Independently tested, not self-certified
ORION Assured
Faction Pods and Portals have been independently tested by ORION for external service exposure, with results documented.
AIS · Assured Information Security
For military, government and enterprise customers that need additional assurance, AIS provides hardware and firmware inspection, reverse engineering and red teaming.
Davolink
Faction's engineering and design partner for Faction Pods & Portals, bringing more than 25 years of Wi-Fi router design and development.
OSec
Vulnerability and patch monitoring through our partner OSec, coming soon.

Leahy Center for Digital Forensics & Cybersecurity
Independent security testing and validation of Faction Pod hardware, platform and architecture, with collaborative research into vulnerabilities.
Which one fits
Same Faction Network, same owner-controlled keys. What changes is where the hardware comes from, how far its assurance goes, and who does the work.
| Attribute | Faction Pods & Portals | Faction Outpost | Faction Canopy |
|---|---|---|---|
| What it is | Faction hardware running Faction firmware | A screened third-party router we prepare, test and ship | Faction enablement and configuration for compatible hardware you already own |
| Hardware | Purpose Built, Assembled in USA, ORION Assured | Third-party, screened and tested by Faction | Hardware you already own: compatible models identified by Faction, or your own choice |
| ORION Assured | Yes | Optional — military, government and enterprise | Not available |
| Who does the work | Faction | Faction | You, or your IT team, MSP or integrator |
| Availability | Pods: pilots and volume pre-orders now. Portals: Q1 2027 | Early Access | Early Access |
Hours or days, not months
Secure OT, IoT & ICS in your owner-controlled Zero Trust Faction Network. No rip-and-replace, no software agents to install, no additional firewalls to configure. Deploy at any site with minimal IT support required.
Inventory and prioritize what's exposed
Inventory the agentless, legacy, OT and IoT devices sitting unprotected on your networks. Prioritize those which are most critical to your operations.
Stand up a Faction Network
Create an owner-controlled Zero Trust network in minutes, with keys and certificates controlled and issued by you.
Deploy Faction protection for critical machines and devices
No software agent, no change to OT, IoT & ICS machines and devices themselves.
- Pods and Portals: scan the QR code, click, adopt.
- Faction Outposts: adopted on your local network with a Faction application.
- Faction Canopy: convert your own hardware.
Isolate, segment and manage
Take vulnerable OT, IoT & ICS off the Internet. Add additional segmentation as needed with Faction Groups. Manage every site and device from one place.
Expand with confidence
Add sites, devices, and users as you grow. Your owner-controlled Faction Network scales to your entire operational footprint.
Industries
Manufacturing
Factory floors, production lines, and industrial sites where uptime, safety, and operational continuity are mission-critical.
Healthcare
Clinical environments with connected devices, equipment, and systems that must stay available and protected — regardless of their age or patchability.
Military & Law Enforcement
Military programs, contractors and suppliers carrying sensitive defense work, where the FCC has warned that the routers they rely on can't be trusted.
Energy & Utilities
Power and utility systems directly targeted by Volt Typhoon and other nation-state actors — where a disruption is a public safety event, not just a data breach.
Critical Infrastructure
Water, transport and building systems, where resilience is a public-safety obligation and not just an IT concern.
Smart Agriculture & Food Production
Farms, processing plants and distributed field sites — remote and often unmanned operations where connectivity is limited but the attack surface is not.
Government & Public Sector
Public infrastructure and citizen-facing services where security and continuity carry legal and public-safety obligations.
Financial Services
Transactions, records and customer trust, where the connected systems in branches and back offices have to stay available and protected.

Own your trust. Keep your peace of mind.
The new threat environment calls for a new Zero Trust model. We'd welcome the chance to show you how Faction puts you in control and secures your critical systems and assets rapidly with low cost and IT overhead.